
The modern web browser has evolved far beyond its original scope as a simple window for viewing static HTML documents. Today, it functions as a comprehensive operating system within an operating system, hosting complex JavaScript runtimes, memory-intensive web applications, and, increasingly, autonomous artificial intelligence agents. These native AI assistants are designed to streamline user workflows by summarizing documents, managing tabs, interacting directly with web applications, and executing multi-step tasks across the internet. However, this deep integration into the core architecture of modern browsers has inadvertently created a vast, high-value attack surface. Security researchers are uncovering architectural blind spots where the very features meant to empower users can be turned against them through subtle manipulation of trusted browser components.
A striking example of this paradigm shift in cyber threats has recently emerged from security disclosures highlighting a sophisticated attack methodology targeting major Chromium-based browsers. Independent security researcher Gal Weizman, operating through Forever Security, unveiled a novel exploitation vector capable of seizing complete control over the embedded artificial intelligence assistants found in some of the world’s most popular browsing environments. This attack class, designated under the moniker "BragJack," demonstrates how a seemingly mundane and unassuming browser extension—once installed on a victim’s device—can bypass traditional security perimeters to command hyper-privileged AI models without triggering user awareness or interaction.
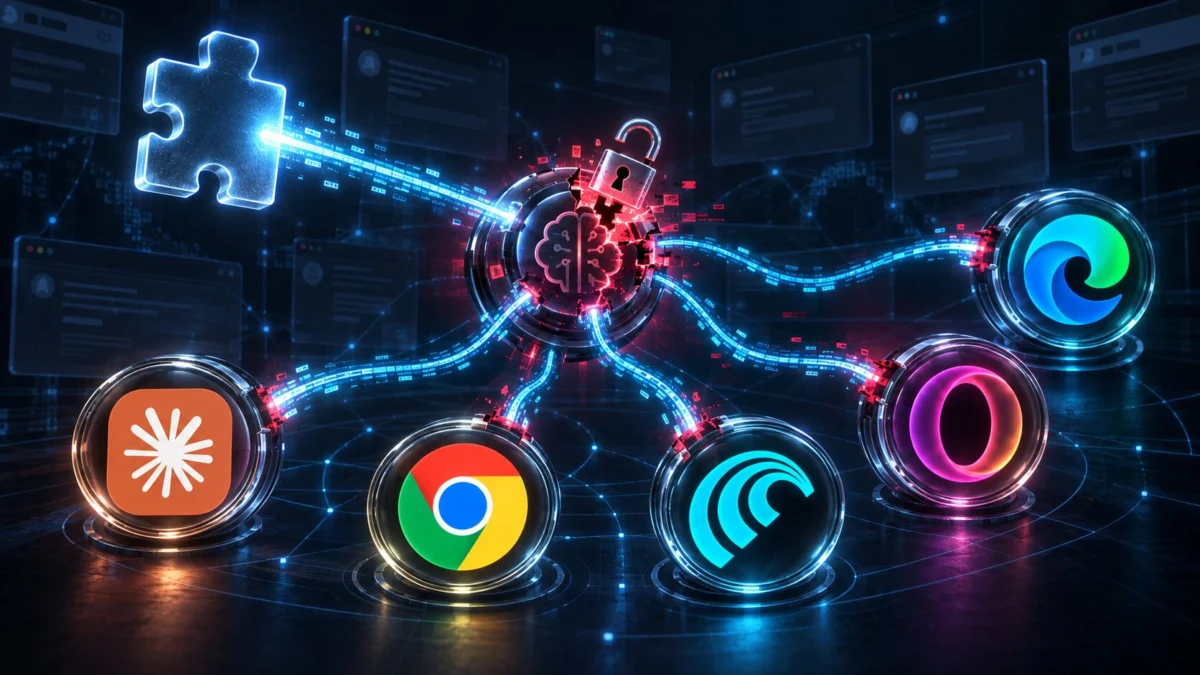
The successful demonstration of BragJack across five distinct platforms—including Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Anthropic’s Claude integration in Chrome—signals a troubling reality for software architects. It underscores the inherent risks of coupling high-capability machine learning models directly with deep system-level APIs without enforcing rigorous, zero-trust isolation barriers between third-party extensions and privileged core utilities.
To fully understand the mechanics behind BragJack, one must examine the structural composition of contemporary AI-augmented browsers. Weizman conceptualizes these advanced systems through a biological metaphor: they possess a "brain" and a "body." The brain corresponds to the underlying large language model or neural network, which ingests instructions, interprets intent, and formulates logical plans. The body, conversely, consists of the privileged internal browser components, native APIs, and system hooks that execute physical actions in the digital environment. These actions range from reading local files and capturing high-resolution screenshots to navigating between web pages, filling out forms, and interacting with Document Object Models (DOM).
The fundamental vulnerability lies in a dangerous trust asymmetry. Historically, browser extension security models were constructed around the assumption that extensions operate within defined sandboxes, interacting primarily with web traffic and page content rather than internal browser daemons. However, as browser vendors rush to embed artificial intelligence deep into the fabric of the application, these boundaries have blurred. Privileged internal components often place a high degree of implicit trust in the web origins and local resources they communicate with, assuming that traffic traversing internal loops or specific application domains is inherently safe from tampering.
BragJack exploits this architectural vulnerability by leveraging Chromium’s native declarativeNetRequest (DNR) functionality. The DNR API is a legitimate, highly useful feature designed to allow extensions to modify how network requests are handled safely, enabling content blocking, privacy enhancements, and header modifications. In the hands of a malicious extension, however, DNR becomes a scalpel for surgical network manipulation. By altering response headers, intercepting internal resource loads, and redirecting web traffic intended for trusted services, an attacker can effectively bridge the gap between an unprivileged extension context and a privileged internal AI subsystem.
In the case of Google Chrome, Weizman discovered that while extensions were strictly blocked from directly interacting with the privileged chrome://glic component or injecting arbitrary scripts into official Google Gemini web endpoints, the application’s underlying architecture was still vulnerable at the network request level. By utilizing DNR rules to weaken security headers and successfully redirecting a critical JavaScript resource, the malicious extension could execute arbitrary code directly inside the Gemini context. This bypassed standard request flows and allowed direct communication with Chrome’s internal AI component. The resulting escalation of privileges granted the attacker the ability to read local files, scrape sensitive web content, capture screenshots, and potentially access hardware peripherals such as webcams and microphones. Google formally acknowledged this architectural oversight, assigning the finding CVE-2026-0628 and awarding the researcher a significant bug bounty.
While reading sensitive local data represents a severe security breach, the implications grow exponentially darker when applied to agentic browsers designed not just to read, but to act. Platforms such as Perplexity Comet and Opera Neon incorporate autonomous agents engineered to execute complex tasks across the web on behalf of the user. These agents do not merely parse information; they navigate websites, execute transactions, and manipulate data streams.
When Weizman turned his analytical focus toward Perplexity Comet, he uncovered an alarming trust relationship regarding secondary domains. The browser’s built-in agent extension implicitly trusted multiple Perplexity domains, including internal testing environments and staging servers that lacked the rigorous security hardening applied to the primary production site. By deploying DNR rules to manipulate redirects, the malicious extension loaded these less-protected domains and successfully injected a content script capable of issuing direct commands to the built-in AI agent.

The consequences of this breach extend far beyond traditional data exfiltration. In practical demonstrations, the researcher forced the Comet agent to independently navigate to Perplexity, access the victim’s private email correspondence, summarize the contents, and stealthily transmit the synthesized data to an external, attacker-controlled destination. Because the agent operated under its legitimate user-granted privileges, the actions appeared entirely authentic to standard monitoring tools, completely bypassing traditional endpoint detection and response (EDR) signatures that look for anomalous binary execution.
Microsoft Edge presented a unique engineering challenge due to the browser’s proactive defensive design choices. Microsoft had deliberately partitioned its AI agent into distinct "Think" and "Do" modes. This architectural segregation was implemented precisely to prevent the model from simultaneously processing arbitrary, potentially malicious instructions and executing real-world actions. By decoupling reasoning from execution, the developers hoped to neutralize prompt injection attacks before they could result in tangible harm.
Despite these safeguards, Weizman successfully engineered an exploit by identifying a critical race condition within the browser’s state management logic. By flooding the application with rapid requests, the attack script could momentarily disable the operational restriction during the prompt injection phase, and then seamlessly re-enable the action capability just before the agent performed its internal state validation check. Microsoft patched this elusive synchronization flaw, issuing CVE-2026-55945 to track the vulnerability. Comparable weaknesses were likewise identified within Opera Neon and Anthropic’s Claude in Chrome extension—highlighting that browser extensions operating as standalone entities face identical architectural pitfalls when interfacing with cloud-based or local AI engines.
This research builds upon a growing body of work exposing vulnerabilities in browser-based AI add-ons. Earlier security analyses targeting the Claude for Chrome extension revealed systemic flaws in how synthetic user interactions were processed. Specifically, the extension executed critical AI workflows based on simulated DOM clicks without cryptographically verifying whether those interface events originated from authentic physical user input. Alarming as it was, the vulnerable code architecture remained exploitable across multiple consecutive software releases, demonstrating the immense difficulty software vendors face in securing complex asynchronous workflows. This followed closely behind disclosures of vulnerabilities like "ClaudeBleed," which highlighted an over-reliance on broad origin trust models rather than strict script-level verification.
To categorize this class of threat accurately, Weizman introduced the concept of "Prompt Forcing." Traditional prompt injection typically relies on indirect methods—such as hiding malicious text within a webpage, an email, or a document that an AI subsequently reads—hoping the model will misinterpret the hidden text as a legitimate command. Prompt Forcing, however, operates on a fundamentally different level. Instead of tricking an AI through passive content ingestion, the attacker directly provisions the agent with a comprehensive prompt and a structured sequence of follow-up instructions from an authoritative local context.
The AI agent, trusting the integrity of the channel through which the instructions arrived, unquestioningly translates those commands into valid browser actions utilizing its pre-assigned system privileges. This distinction holds profound implications for modern endpoint defense strategies. Traditional security solutions are fundamentally built to detect malicious binaries, unauthorized memory injections, or illicit network connections. In a Prompt Forcing scenario, none of these indicators are present. The software executing the harmful action is entirely legitimate, running authorized code, and leveraging sanctioned APIs. The attack succeeds not because the code is malicious, but because the control plane has been subverted.
The emergence of vulnerabilities like BragJack illuminates a systemic challenge facing the cybersecurity industry as artificial intelligence transitions from a novelty feature into the foundational operating layer of consumer and enterprise software. As browsers and operating systems grant software agents increasingly broad autonomous capabilities, the attack surface expands in lockstep. A compromised extension that historically posed a localized risk—such as tracking web browsing habits or modifying page layouts—can now transform into a direct pathway to sensitive local files, personal communications, and automated digital agency.
Mitigating these deeply rooted architectural risks requires a fundamental shift in how developers design agentic software. Browser vendors must move beyond superficial permission prompts and adopt rigorous, zero-trust isolation boundaries between unprivileged extension environments and internal AI execution contexts. Furthermore, automated agents must be engineered to demand cryptographic verification for intent, ensuring that autonomous actions cannot be triggered by unauthorized local scripts regardless of network path manipulations.
For end users navigating this increasingly complex threat landscape, maintaining robust digital hygiene has never been more critical. Security best practices dictate keeping browsers and all associated extensions meticulously updated to the latest stable versions to ensure rapid patch deployment. Users should also conduct regular audits of their installed browser extensions, immediately removing any tools that are unrecognized, deprecated, or no longer actively maintained. Most importantly, individuals must exercise extreme skepticism toward broad, sweeping permission requests—particularly extensions demanding the ability to "read and change all your data on all websites"—as these hyper-privileged permissions form the foundational stepping stones for advanced multi-stage attacks like BragJack.
