
Modern software supply chain security faces an unprecedented velocity threat, as academic researchers have revealed that sensitive credentials, API tokens, and cloud access keys embedded within public container images can be harvested and weaponized by malicious actors in under eight seconds. This alarming finding underscores the relentless efficiency of automated threat infrastructure constantly scanning public repositories like Docker Hub for accidental secrets disclosure.
The research, conducted by Stony Brook University academics Billy Tsouvalas and Nick Nikiforakis, provides a terrifying window into the automated underworld of cloud exploitation. To measure the exact speed and scale of credential harvesting in modern DevOps environments, the researchers deployed a comprehensive honeypot experiment. Over a meticulous four-month evaluation period, they published a total of 300 intentionally flawed container images across eight distinct public container registries.

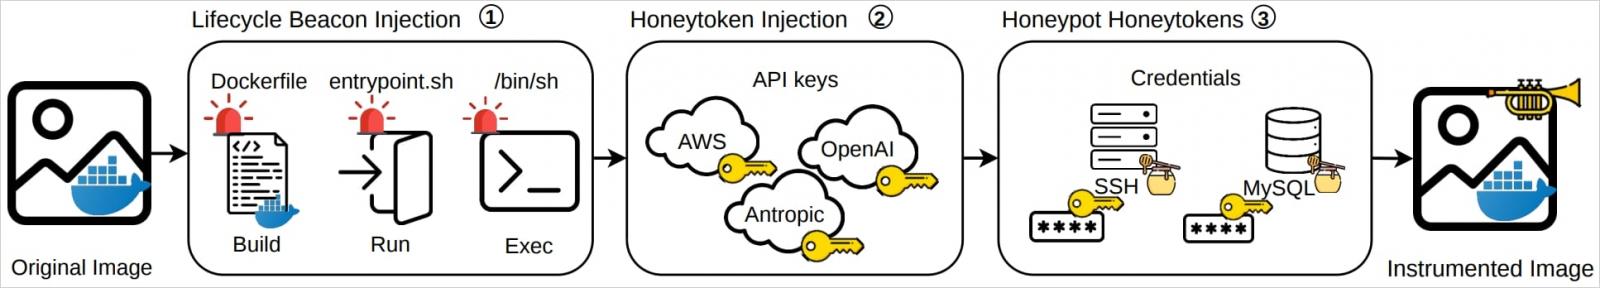
These decoy packages were loaded with a variety of high-value secrets, including Amazon Web Services (AWS) programmatic access keys, generative artificial intelligence tokens from OpenAI and Anthropic, as well as simulated Secure Shell (SSH) private keys and database credentials. To capture every interaction, the researchers embedded sophisticated telemetry and detection mechanisms designed to trigger notifications whenever a container image was pulled, built, instantiated, or subjected to shell access.
The results of the experiment, presented at the prestigious ACM Conference on Computer and Communications Security (CCS), expose a frighteningly automated ecosystem. Throughout the four-month window, the honey-images were pulled more than 75,000 times by outside entities. More critically, the embedded AWS access keys triggered an astonishing 140,000 API calls originating from approximately 5,000 unique IP addresses worldwide.
The behavioral patterns observed in the incoming AWS traffic revealed a systematic approach to cloud resource abuse. Automated scripts immediately tested the validity of the harvested credentials, proceeded to enumerate available cloud assets, and in many instances, began aggressively consuming infrastructure resources. The absolute fastest exploitation timestamp recorded during the study was a mere 7.86 seconds following the initial publication of a container image on Docker Hub.

Furthermore, the data demonstrated widespread systemic vulnerability: the median time elapsed before the first unauthorized API call occurred was roughly 51 seconds, and every single one of the 100 planted AWS credentials had been actively exploited within 15 minutes of going live. High-value artificial intelligence tokens fared no better; exposed OpenAI and Anthropic keys were immediately hijacked by opportunistic actors, leading to the rapid depletion of test-account balances. While the vast majority of this aggressive scanning and exploitation activity concentrated on Docker Hub, other platforms like Harbor also registered notable instances of credential abuse.
To better understand how these threat actors operate, the researchers analyzed the underlying mechanisms of the automated tools interacting with their honeypots. They broadly classified these autonomous discovery tools under the umbrella term "ContainerBots," though they noted that the scans lacked coordination, pointing to numerous independent threat actors and opportunistic botnets operating concurrently. Interestingly, telemetry logs revealed that the decoy containers were almost never actually run or instantiated within an execution environment.
This absence of runtime execution led the academics to a critical conclusion: unauthorized actors are not executing malicious code or spinning up containers to look for secrets; instead, they are relying entirely on advanced static analysis techniques. By systematically unpacking container image layers or querying registry APIs directly to extract filesystem contents, automated scrapers can scour multi-layered images for plain-text secrets in fractions of a second, bypassing traditional runtime monitoring tools entirely.
The implications of this study extend far beyond an academic exercise, holding a mirror up to pervasive security hygiene issues within the broader software development lifecycle. Accidental credential leaks—frequently caused by developers failing to properly configure .dockerignore files, leaving secrets in build arguments, or committing environment configuration files directly into container layers—remain an endemic problem. Once a high-privilege cloud key or corporate authentication secret is exposed in a public repository, revoking it and cleaning up the resulting fallout requires immense cross-functional coordination, often leaving organizations exposed to lateral movement and data exfiltration long before the leak is discovered.
Despite notifying platform operators such as Docker in May with exhaustive documentation of their findings, the researchers report a disappointing lack of substantive institutional response beyond a standard acknowledgement. A follow-up validation experiment conducted in August confirmed that no meaningful automated defenses or preventative architectural changes had been implemented on the platform to mitigate the rapid leakage vector.
To combat this pervasive threat, the Stony Brook researchers have urged container registry operators to adopt proactive defense-in-depth measures. Chief among their recommendations is the implementation of mandatory, automated secret-scanning pipelines that inspect container layers for sensitive material prior to making packages publicly accessible, coupled with immediate warning systems to alert publishers of exposed secrets. Additionally, they suggest that registries implement rate-limiting or access controls on public feeds of recently published or updated images, which would significantly hinder the efficiency of mass-scanning tools operated by malicious actors. Until major repositories adopt these baseline security controls, developers and organizations must implement rigorous internal pre-commit hooks and local static analysis tools to ensure that cloud keys never make it to public registries in the first place.
