
The modern digital threat landscape is routinely shaped by forgotten software artifacts, left behind on user endpoints long after their underlying ecosystems have dissolved. A striking demonstration of this phenomenon unfolded when a coalition of threat intelligence researchers executed a meticulously planned remediation operation to neutralize a critical vulnerability residing inside an abandoned iteration of the once-ubiquitous Popcorn Time ecosystem. Formally cataloged as CVE-2026-30612, the security flaw possessed the harrowing potential to facilitate widespread remote code execution (RCE) with the highest possible privileges across millions of desktop environments running Windows and macOS. The incident underscores a sobering reality of contemporary computing: applications installed years prior, forgotten by their operators and neglected by their users, can quietly evolve into existential strategic assets for threat actors seeking large-scale botnet infrastructure.
The vulnerability itself was rooted in the automated updater mechanism utilized by Time4Popcorn, a popular unauthorized fork of the original Popcorn Time BitTorrent streaming platform. During its peak adoption phase, the application captivated millions of users globally by marrying peer-to-peer file-sharing protocols with a polished, subscription-style user interface that rivaled legitimate legal services like Netflix. However, as regulatory pressure and intellectual property enforcement forced the original project creators to abandon the codebase, a fragmented array of derivative forks emerged to fill the vacuum. Time4Popcorn rapidly captured a massive share of this illicit streaming market, distributing client software built on a fragile architectural foundation that ultimately laid the groundwork for a catastrophic supply chain hazard.
At the core of the technical failure was the updater’s reliance on unencrypted HTTP communications to query an abandoned command-and-control infrastructure domain, specifically popcorntimeupd.xyz. Compounding this foundational transport-layer vulnerability was the application’s fatal design flaw: the updater accepted and executed binary packages retrieved from this remote server without performing any cryptographic digital signature verification. In practical security terms, any malicious entity capable of hijacking the domain—whether through domain name system (DNS) manipulation, expired domain acquisition, or network-level adversary-in-the-middle positioning—could seamlessly inject arbitrary payloads into the update pipeline. Because the application executed these updates with elevated system privileges—running as SYSTEM on Microsoft Windows environments and root on Apple macOS distributions—a successful exploit would grant an attacker total, unrestricted control over the underlying operating system.
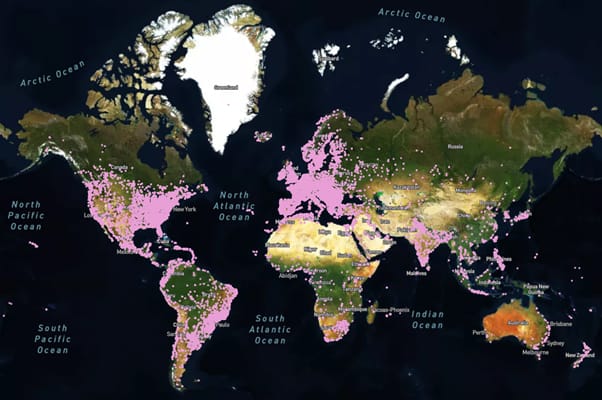
The scale of the potential disaster only became fully apparent when security specialists at Eye Security initiated an investigative operation after acquiring the dormant domain. Upon taking control of the infrastructure, the researchers were met with an unprecedented torrent of incoming telemetry requests. Telemetric monitoring revealed that approximately three million Windows client instances and an additional 350,000 macOS instances were actively attempting to poll the defunct update server. An exhaustive analysis of the connecting IP addresses and telemetry data uncovered an alarming distribution profile. Connections originated not merely from typical consumer residential internet service providers, but also heavily from enterprise environments, government agencies, and critical military networks. Interestingly, deep diagnostic inspection indicated that the vast majority of these client instances were entirely dormant; users had long since ceased actively consuming media through the software, leaving the binaries installed and forgotten in the dark corners of their hard drives.

Faced with the terrifying prospect of what could happen if this dormant cyber weapon fell into the hands of state-sponsored advanced persistent threat (APT) groups, financially motivated ransomware syndicates, or commercial botnet operators, the research team resolved to take unprecedented preemptive action. Operating under strict legal and ethical parameters, the specialists designed an intervention strategy that effectively utilized the application’s own flawed update architecture against itself. Between November 2025 and March 2026, the team engineered a benign remediation payload delivered via the hijacked domain mechanism. Rather than weaponizing the vulnerability for malicious objectives, the patch was specifically coded to cleanly terminate and permanently disable the vulnerable background update service.
Executing this defensive operation was fraught with technical and operational hurdles. During the initial staging and testing phases, security products and endpoint detection and response (EDR) solutions frequently flagged the remediation payload as suspicious or outright malicious, largely because the binary’s core function was to forcibly terminate and modify a running system service. The researchers were forced to iteratively refine their code to ensure it operated transparently without triggering false positives across commercial security software suites, while strictly adhering to data privacy and integrity standards. The payload was engineered to be entirely non-destructive: it collected zero telemetry or host data, and it refrained from deleting user files or altering unrelated system configurations, maintaining a strictly benign footprint.
The intervention yielded immediate and dramatic results. Following the deployment of the remediation script, the infrastructure recorded over two million successful update downloads as dormant clients eagerly ingested the healing payload. By March of the following year, incoming connection requests directed at the update domain plummeted by an astonishing 98 percent, effectively defusing a ticking time bomb that had threatened millions of global endpoints. To ensure long-term stewardship and prevent any subsequent malicious actors from reclaiming the infrastructure, ownership of the domain was formally transferred to The Shadowserver Foundation, a reputable non-profit security organization renowned for managing sinkholes and cleaning up compromised cyber assets.
Despite the remarkable success of this operation, industry experts are quick to emphasize that the underlying threat has not been entirely eradicated. The remediation effort carried out by the research team faced inherent platform limitations, most notably concerning mobile environments. Android users who had previously downloaded and installed the mobile iteration of the Time4Popcorn application remain dangerously exposed. Because Android architecture and the specific mechanics of the mobile app required active user interaction to authorize and install updates, the researchers were technically incapable of deploying a remote, silent fix for mobile devices. Consequently, countless Android smartphones and tablets continue to run compromised versions of the software.
Compounding the lingering risk on desktop platforms is the profound architectural decay of the application’s internal rendering engine. The Time4Popcorn client was built upon an egregiously outdated version of the Chromium browser engine dating back to 2014. This antique engine completely lacks modern browser sandbox protections, memory safety mitigations, and vulnerability patches released over the past decade. Even with the automated updater successfully disabled, the presence of such a prehistoric, unpatched rendering engine on a machine opens up a secondary vector for exploitation. If an attacker were to somehow deliver local code execution or chain the software with other browser-based vulnerabilities, the compromised application could serve as a direct gateway to full system compromise.
From a broader industry perspective, this incident casts a glaring spotlight on the persistent dangers of "shadow IT" and orphaned software ecosystems. Millions of consumers regularly download third-party applications, utilities, and media clients from unofficial repositories, frequently granting them elevated permissions during the initial installation wizard. Once the utility of the software expires or the developers abandon the project, the applications linger indefinitely in the background of operating systems. This creates a vast, unmonitored attack surface characterized by forgotten binaries, unmaintained libraries, and abandoned network infrastructure. When digital certificates expire, domains lapse, or registration information decays, these digital ghosts become prime targets for opportunistic threat actors looking to bootstrap large-scale cyber attacks with minimal effort.
Cybersecurity analysts and incident responders warn that software supply chain security must extend far beyond active development pipelines and corporate code repositories. The lifecycle management of software does not magically conclude when developers stop writing code or when a company shuts down its operations. As long as compiled binaries remain resident on consumer and enterprise endpoints, they represent persistent liabilities that can be weaponized against the host machine. Organizations must implement robust endpoint management policies, utilize advanced asset discovery tools to sniff out unauthorized and legacy software, and enforce stringent application control protocols to prevent dormant, high-privilege applications from lurking undetected within their perimeters.
Ultimately, the successful neutralization of the Time4Popcorn threat serves as both a cautionary tale and a masterclass in proactive threat mitigation. It demonstrates the profound ingenuity required by modern security researchers to combat systemic cyber risks, while simultaneously highlighting the precarious nature of our interconnected digital infrastructure. For the millions of everyday computer users who casually download unverified applications for convenience or illicit media consumption, the episode offers a stark and uncompromising lesson. The definitive remedy for this and similar security crises remains starkly straightforward: users must manually audit their operating systems, identify legacy software remnants, and permanently purge abandoned applications from their devices before dormant code is awakened by malicious hands.
