
The contemporary landscape of cybercrime has evolved far beyond conventional malware injections, enterprise data exfiltration, and targeted ransomware sieges. A more pervasive, insidious vector of financial exploitation has taken root across the global digital ecosystem, capitalizing heavily on human psychology, consumer fatigue, and the inherent trust placed in household commercial names. Recent threat intelligence findings released by digital risk protection authorities reveal an alarming escalation in automated, highly modular fraud schemes centered around fraudulent reward portals and fabricated gift card campaigns. These operations, scaling into thousands of distinct tracked incidents, do not merely target isolated enterprise networks; they actively subvert the digital identities of preeminent retail, gaming, and technology institutions to fleece unsuspecting web users.
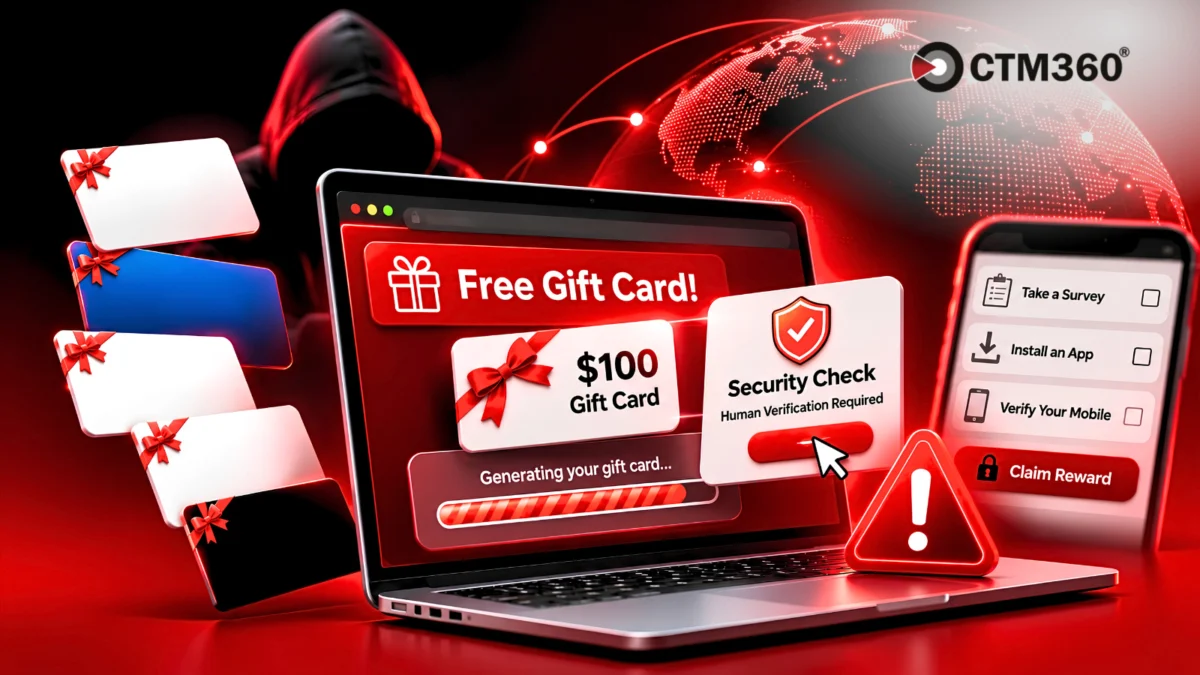
At their core, these schemes rely on an exceptionally straightforward psychological hook that exploits consumer desires for economic relief amid inflationary pressures. Victims are systematically targeted through high-reach social media channels, banner ads, and sponsored posts featuring manipulated celebrity endorsements. The pitch is enticingly simple: a prominent global brand—ranging from e-commerce giants like Amazon and Walmart to lifestyle platforms such as Sephora, SHEIN, and gaming ecosystems like PlayStation—is supposedly running a limited-time promotional giveaway. To claim a high-value digital voucher, the recipient merely needs to follow an external redirect link, answer a brief promotional survey, and successfully navigate a purportedly minor security confirmation step known as "human verification."
Beneath this polished veneer of high-definition corporate graphics, convincing progress bars, and fabricated testimonial feeds, however, lies an industrial-grade affiliate monetization machine. The infrastructure driving these campaigns is completely untethered from the actual brands being impersonated. No physical or electronic gift cards exist within the operational pipeline. Instead, the entire architecture is purposefully engineered to pipeline consumer traffic through a sophisticated sequence of fraudulent loops, harvesting Personally Identifiable Information (PII), enforcing forced application installs, and covertly enrolling victims into recurring, high-cost mobile subscription services that bill their cellular accounts without explicit, informed consent.
Deconstructing the Modular Infrastructure of Mass Brand Impersonation
One of the defining characteristics of this modern fraud wave is its structural agility. Traditional phishing campaigns often require bespoke landing pages, specialized credential-harvesting kits, and infrastructure meticulously tailored to a single enterprise target. In stark contrast, the operations documented by digital risk specialists utilize a highly decoupled, modular framework. Threat actors have successfully separated the front-end marketing layer from the back-end revenue-generation engine.
This modularity allows cybercriminal syndicates to execute rapid rotation strategies. If a specific domain is flagged, blocked by web filters, or taken down by hosting providers, the operators can pivot almost instantaneously. By swapping out the impersonated corporate identity, changing the underlying promotional imagery, updating the celebrity hook, and spinning up a fresh domain name, the core scam engine remains fully operational with negligible downtime. Analysts tracking this continuous activity have mapped over a thousand unique incidents sharing identical infrastructural fingerprints, underscoring the industrialized nature of these syndicates.
The choice of impersonated brands is calculated to maximize demographic reach. By utilizing retail platforms with broad, diverse consumer bases, the threat actors ensure that a high percentage of individuals who land on the malicious pages already maintain a legitimate relationship or familiarity with the brand. This familiarity immediately lowers the user’s defensive skepticism. When an interface prominently displays the official logos, color schemes, and trademarked imagery of a trusted multi-billion-dollar enterprise, the cognitive dissonance required to question the legitimacy of a "free $500 gift card" offer is significantly reduced.
The Psychological Progression of the "Fake Generation" Trap
Navigating the user journey within these fraudulent portals reveals a carefully orchestrated manipulation of human behavior, systematically moving targets through distinct psychological phases: curiosity, artificial validation, and urgent pressure. The lifecycle of the fraud begins the moment an individual clicks an ad promising unearned financial value.
Upon arrival at the fraudulent landing site, the user is greeted by an interface designed to mimic an authentic enterprise promotional portal. To bolster credibility, these web properties frequently incorporate dynamic elements such as live visitor counters, recent activity logs showing other users successfully claiming rewards, and countdown timers creating a false sense of scarcity. The user is then prompted to select their preferred gift card denomination, initiating the next phase of the deception: the simulated generation sequence.
Once a value is selected, the portal initiates a scripted, highly visual progress animation on the front end. This animation employs progress bars, loading spinners, and technical-looking status updates ("Connecting to secure database…", "Validating promotional token…", "Allocating voucher hash…") to trick the victim into believing complex backend cryptographic processes are actively retrieving their gift card.
The climax of this psychological trap arrives when the system displays a partially masked digital code—for instance, a sequence formatted as XXXX-XXXX-7F3A-XXXX. By revealing a portion of the alphanumeric code while obscuring the rest, the operators leverage a classic cognitive bias: the illusion of proximity. The user is visually convinced that the reward is real, tangible, and literally seconds away from being fully revealed. However, right before the final digits are unlocked, the interface introduces an absolute barrier: the mandatory "Security Check" or "Human Verification" gate.
The Endless Verification Loop and the Mechanics of "Trap 10"
The purported human verification process serves as the central pivot point where the operation transitions from a branding charade into active financial monetization. Rather than employing standard, frictionless mechanisms such as CAPTCHA challenges or device-fingerprinting checks, the verification protocol forces the victim into a relentless, circular labyrinth of third-party commercial offers—a phenomenon categorized by threat analysts as "Trap 10."
Instead of confirming humanity, the verification gate redirects the user through a dense thicket of external activities. Victims are told they must complete a series of mandatory tasks to prove they are not automated bots. These tasks typically include:
- Completing lengthy, data-harvesting market research surveys that sell off consumer preferences to third-party data brokers.
- Downloading and installing unverified mobile applications, potentially exposing their smartphones to adware or tracking SDKs.
- Registering for dubious third-party sweepstakes and promotional contests under the guise of winning secondary prizes.
- Submitting mobile telephone numbers and verifying them via PIN or One-Time Passwords (OTPs) under the false pretense of confirming identity.
Throughout this entire ordeal, the system maintains the illusion that completion of these tasks will instantly release the remainder of the gift card code. Yet, in empirical testing across hundreds of observed iterations, no reward is ever delivered. If a user successfully completes a required survey or downloads an application, the portal simply refreshes, marks the step as "incomplete" due to a supposed network error, or loops the victim into an entirely new set of commercial demands. The user remains trapped in an endless loop of labor and data surrender, chasing a reward that was never designed to materialize.
The Economics of Volume: Affiliate Hand-Offs and Commission Networks
Understanding why these operations persist at such an industrial scale requires examining the underlying financial incentives. Unlike traditional credential theft, where attackers monetize stolen data through illicit marketplaces or account takeovers, gift card scam networks operate entirely on a performance-based affiliate marketing model.
When a victim is redirected through the various verification hurdles, they are not merely clicking random links; they are traversing sophisticated affiliate tracking architectures. The URLs embedded within the lure pages incorporate specialized tracking parameters, such as unique offer identifiers (offer_id) and affiliate identifiers (aff_id). These digital tokens ensure that every action taken by the victim—whether it is installing an application or submitting a mobile number—is cryptographically attributed to the threat actor’s account within a commercial affiliate network.
The monetization peaks when a victim falls for the mobile subscription trap. By entering their cellular number and completing an OTP verification, the user unwittingly authorizes micro-billing agreements or premium-rate SMS subscription services operated by shady billing aggregators. Behind the scenes, the affiliate network credits the threat actor with a substantial bounty or commission for every successful conversion. Multiply this payout by thousands of daily victims across multiple global jurisdictions, and the financial yield for the cybercriminal syndicates becomes immense, funding further infrastructure expansion and advertising campaigns on mainstream social media platforms.
Collateral Damage: Impact on Consumers and Enterprises
The downstream consequences of these fraudulent campaigns extend far beyond the immediate frustration of wasted time and unrealized rewards for the individual consumer. The personal fallout is multifaceted and enduring. Victims who engage with these portals frequently suffer from a severe compromise of their digital privacy. The PII submitted during fake verification steps—including email addresses, home addresses, and phone numbers—is immediately archived, aggregated, and traded among spam networks, resulting in an overwhelming influx of unsolicited marketing calls, phishing emails, and smishing attacks. Furthermore, those who fall victim to mobile billing scams often discover unexpected, recurring charges on their monthly carrier statements, necessitating arduous dispute processes with mobile service providers.
Simultaneously, the implications for enterprise organizations whose brands are weaponized in these campaigns are severe. The widespread proliferation of fraudulent giveaways representing established corporate identities inflicts tangible harm on brand equity and consumer trust. When thousands of everyday consumers encounter persistent, scam-ridden advertisements bearing the name and likeness of a trusted retail platform, their baseline perception of that brand’s digital security and customer care is inevitably tarnished. Many consumers mistakenly hold the impersonated company accountable for failing to stop the fraud, leading to customer churn, negative public relations, and a degradation of brand loyalty.
Furthermore, corporate security teams find themselves caught in a reactive posture. Because the underlying infrastructure utilizes decentralized, rapidly shifting domains hosted across disparate cloud providers and content delivery networks, traditional takedown requests can be sluggish and ineffective. By the time a registrar revokes a malicious domain, the threat actors have already migrated their campaign assets to a dozen newly registered alternatives.
Mitigation, Defense, and the Future of External Digital Risk Protection
Addressing the relentless expansion of brand-impersonation gift card scams requires a fundamental shift in defensive strategy. Traditional perimeter security controls, endpoint protection platforms, and internal network monitoring tools offer little to no visibility against threats that operate entirely within the external digital landscape—outside the organizational firewall.
To effectively counter these sophisticated campaigns, enterprises must adopt proactive Digital Risk Protection (DRP) methodologies. This involves continuous, automated monitoring of the broader internet, social media networks, application stores, and domain registration registries for unauthorized uses of corporate intellectual property, logos, and brand nomenclature. By identifying fraudulent domains and phishing landing pages at the moment of inception—often during the initial DNS registration or social media ad placement phase—security teams can initiate rapid takedowns and disrupt the affiliate pipelines before they achieve critical mass.
Moreover, consumer education remains a critical line of defense. As threat actors continually refine their social engineering tactics, leveraging AI-generated imagery, hyper-targeted ad placements, and increasingly convincing user interfaces, public awareness campaigns must emphasize core verification principles. Consumers must be continually reminded that legitimate global enterprises do not distribute high-value monetary vouchers through unverified social media redirects, nor do they require users to complete endless third-party tasks and subscription sign-ups to claim earned rewards.
Ultimately, the battle against automated brand abuse and fraudulent reward portals represents a new frontier in cybersecurity. As long as affiliate monetization schemes yield high returns with minimal operational risk, threat syndicates will continue to refine and scale their operations. Mitigating this pervasive threat demands a collaborative approach combining advanced external threat intelligence, aggressive cross-industry domain enforcement, and heightened consumer vigilance across the global digital ecosystem.
