
The modern threat landscape is continuously evolving, shifting away from traditional, easily detected perimeter breaches toward sophisticated supply-chain compromises and developer-ecosystem abuse. A newly uncovered, highly calculated malware campaign exemplifies this troubling paradigm shift. By systematically weaponizing search engine optimization (SEO) techniques and legitimate developer platforms, malicious actors have begun distributing a previously undocumented information-stealing payload designated as the Rapuncel infostealer.
Joint intelligence findings compiled by threat research teams at LastPass and Delphos Labs have shed light on this sprawling multi-tiered operation. The campaign does not merely target a single corporate identity; rather, it casts a wide net, impersonating the brand equity of LastPass Authenticator alongside at least 39 other prominent technology and software enterprises. By masquerading as indispensable developer tools, utilities, and security applications, the perpetrators have constructed a formidable trap designed to catch unwary users and corporate professionals alike.
What makes this campaign particularly alarming is not just the novelty of the Rapuncel infostealer itself, but the sheer technical complexity of the accompanying delivery architecture. Alongside the primary data-harvesting payload, the malicious repositories deliberately dispense a Microsoft-signed kernel-level driver. This driver possesses the devastating capability to systematically neutralize up to 145 distinct antivirus solutions and enterprise endpoint detection and response (EDR) agents. In doing so, the campaign illustrates a terrifying evolution in commodity malware tradecraft, bridging the gap between basic credential theft and full-scale kernel-level dominance.
Anatomy of an SEO-Driven Supply-Chain Attack
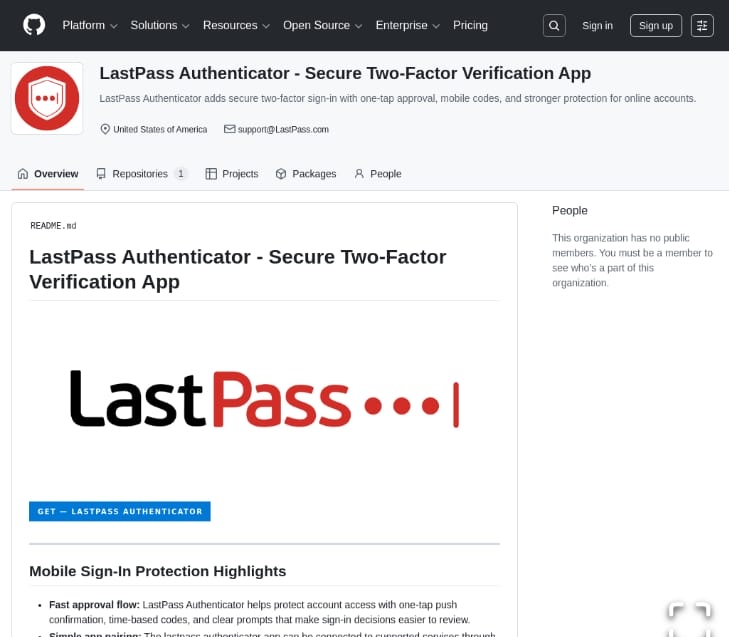
The mechanics of the Rapuncel campaign rely heavily on social engineering combined with tactical search engine manipulation. The attack chain typically initiates when an unsuspecting target—often an enterprise worker, developer, or technical enthusiast—searches online for legitimate tools like the LastPass Authenticator or other high-profile software packages. Through aggressive search engine optimization and potentially compromised or spoofed hosting infrastructure, the threat actors ensure that fraudulent GitHub repositories rank prominently among search results.
Upon navigating to these counterfeit repositories, victims are greeted by professionally styled documentation and repository layouts that closely mimic legitimate open-source projects. However, the seemingly benign download buttons embedded within these pages are rigged. Clicking these links triggers a complex sequence of HTTP redirections, routing the user through a maze of intermediary servers before finally landing on the ultimate payload-delivery infrastructure.
To thwart automated security scanners and sandbox environments, the threat actors implement aggressive file-inflation tactics. The ZIP archives delivered to victims are artificially padded with junk data, swelling in size to as much as 148 megabytes. Many automated analysis pipelines struggle or time out when processing files of this magnitude, allowing the malicious archive to bypass initial gateway filters and email security checks.
Once extracted, the contents of the archive reveal a clever exercise in living-off-the-land techniques and binary sideloading. The core installer provided within the package is actually a legitimate, unmodified copy of the Microsoft Visual Studio CoreCLR Debugger, commonly known as vsdbg.exe. The attackers rename this executable and configure it to perform DLL sideloading, forcing the application to load a malicious dynamic-link library named vsdbg.dll. This sideloaded component acts as the orchestrator, silently deploying both the Rapuncel infostealer and the malicious kernel driver, designated as Alinubx.sys, into the host operating system.
The Kernel-Level Threat: Neutralizing Modern Defenses
Perhaps the most technically sophisticated and dangerous aspect of the Rapuncel campaign is the deployment of the Alinubx.sys driver. Disguised cunningly as a legitimate NVIDIA system component under the filename nvfsflt64.sys and registering itself as the NvFsFilter service, this driver operates in ring 0—the highest privilege level of the Windows operating system.
According to deep-dive analyses provided by security researchers, the driver functions as an aggressive EDR killer. It contains a hardcoded, comprehensive catalog of 145 distinct antivirus, firewall, and endpoint detection and response processes. When executed, the driver deliberately targets these security frameworks to blind the host system before the primary infostealer begins its harvest.
The method by which Alinubx.sys achieves this destruction highlights systemic challenges in operating system security models. LastPass analysts noted that the driver invokes the Windows kernel API function ObOpenObjectByPointer with the AccessMode parameter set to KernelMode. This specific execution path completely bypasses standard user-mode security checks, such as SeAccessCheck, during the handle-opening phase.
By commanding the kernel to open targeted security processes directly as kernel-level code, the driver acquires the authority to terminate them outright. This mechanism successfully neutralizes Protected Process Light (PPL)—a foundational security feature relied upon by modern EDR and antivirus vendors to prevent unauthorized termination, even by users possessing administrative privileges.
Compounding this threat is the provenance of the driver itself. The Alinubx.sys binary used in this campaign is cryptographically signed through Microsoft’s official Windows Hardware Compatibility Publisher certificate chain. Furthermore, at the time of discovery, the driver had not yet been integrated into Microsoft’s vulnerable driver blocklist (HVCI/WDAC blocklists). This legitimate digital signature allows the malicious driver to load successfully on modern versions of Windows that enforce strict driver-signing policies, effectively granting the malware a VIP pass past core operating system security gates.
Forensic examination of the driver code revealed even broader capabilities. Researchers discovered dormant routines within Alinubx.sys designed for file and registry hiding, arbitrary DLL injection, driver and process interception, network traffic manipulation, and port redirection. Although these additional features appear inactive in the current iteration of the campaign, their presence suggests that the threat actors maintain a modular framework capable of transforming the compromised endpoint into a deeply entrenched persistent backdoor.
Inside the Rapuncel Infostealer
With the host system’s security infrastructure effectively neutralized, the Rapuncel infostealer initiates its primary mandate: exhaustive data extraction. Once executed, the malware systematically scours the compromised machine for sensitive assets.
While information stealers typically target standard artifacts such as browser cookies, saved credentials, autofill data, cryptocurrency wallet extensions, and session tokens, Rapuncel incorporates advanced logic to defeat contemporary browser protections. Modern web browsers—particularly Chromium-based applications like Google Edge and Chrome—utilize robust security measures known as app-bound encryption to protect local credential stores from unauthorized programmatic access.
To overcome this hurdle, Rapuncel executes a precise bypass strategy. It injects a specialized helper DLL directly into the target browser process and subsequently invokes its own custom Elevation Service. This technique allows the malware to circumvent app-bound encryption controls, granting it unhindered access to decrypted user credentials and sensitive session tokens stored within the browser database.
Once all targeted data has been gathered, Rapuncel compresses the harvested files into an archive. This payload is then exfiltrated to an external command-and-control endpoint located at 2.26.126[.]50, utilizing standard HTTP-formatted requests transmitted over a raw TCP socket connection.
To ensure long-term viability within the enterprise or consumer environment, Rapuncel establishes system persistence across reboots by registering itself as a dedicated Windows service. As a secondary resilience measure, the malware’s persistence routine continuously monitors the system state. If any security software manages to recover or restart following a system reboot, the persistent service preemptively terminates the defense mechanisms yet again before allowing the core infostealer processes to execute.
Attribution telemetry gathered during the investigation indicates with moderate confidence that Rapuncel shares strong lineage markers with BoryptGrab, a known infostealer family. Additionally, telemetry uncovered that the initial loaders distributing the malware were compiled utilizing the Cruciferra PUROSANGUE crypter, highlighting the underground commercial availability of advanced evasion toolkits to low-tier cybercriminal syndicates.
Strategic Implications for Cybersecurity and Software Supply Chains
The emergence of the Rapuncel campaign underscores critical vulnerabilities in how modern users discover and consume software, as well as the inherent risks associated with trusting decentralized developer platforms. GitHub and similar code-sharing repositories have increasingly become fertile ground for threat actors. By leveraging search engine optimization to hijack high-intent software search queries, attackers effectively bypass traditional perimeter defenses, tricking users into willingly downloading and executing malicious code.
Furthermore, the abuse of legitimate digital certificate signing chains poses an existential dilemma for the security industry. When malicious actors can leverage valid publisher certificates to execute kernel-level code capable of disabling foundational EDR protections, the traditional trust-on-first-use paradigm surrounding signed binaries breaks down. This trend calls for accelerated adoption of hardware-backed behavioral analysis, anomaly detection, and continuous validation of driver legitimacy beyond mere cryptographic signature verification.
Mitigating threats of this caliber requires a multi-layered defense strategy spanning organizational policy, user education, and endpoint hardening. Enterprises must enforce strict application whitelisting policies and restrict user privileges to prevent the execution of unverified software downloaded from public repositories. Additionally, security teams should monitor for anomalous kernel-driver loads, unexpected process termination patterns, and unauthorized modifications to system services.
End users and technical professionals must exercise extreme caution when sourcing utilities, authentication tools, or developer packages online. Security best practices dictate that software should exclusively be acquired directly from official vendor domains, avoiding promotional search engine advertisements and unverified community repositories entirely. As threat actors continue to refine their supply-chain poisoning techniques, maintaining an uncompromising posture of zero trust toward third-party downloads remains the most effective defense against sophisticated information-stealing campaigns.
